I was unsure which title to begin with, as “Verizon DBIR 2026: the social engineering number everyone missed” was not so impactful (yk, I’m a strategist 🤣) and “What does the Verizon DBIR 2026 reveal about social engineering and mobile phishing?” sounded a bit too floooom (which is not a word, synesthetic me just understands).
Next time will A/B test on you 😉
Soooo, the 2026 Data Breach Investigations Report dropped this week. Nineteenth edition. 31k analyzed incidents, more than 22k confirmed breaches (rounded down and nearly double last year’s 12k). The headline everywhere: vulnerability exploitation finally knocked credential abuse off the top spot.
Ok, masses were in the wild but that is not the story! That is the story they want you to read while the actual one runs past you on the mobile lane.
I have been waiting for this report for the wrong reasons
I have been doing offensive work for over [insert here, they’re too many] years, I have written initial-access tooling that nobody knew was running until I told them, I have phished XXXXXXXXX 500 boards from a hotel lobby on a Sunday and when Verizon ships the DBIR I do not read it for the headlines, I just read it for what the headlines bury.
This year they buried a beauty.
Page-two-ish, in the human element section: 62% of breaches involved a human element, social engineering accounted for 16% of breaches, and the median success rate was 40% higher in mobile-centric phishing attacks than via email.
Read that again. Sloooowly.
Mobile phishing success rate is forty percent higher than email.
The industry spent two decades hardening the inbox: Microsoft, BigG, Proofpoint, Mimecast, all billions in tooling. We trained users to hover before they click and we taught them to look for the misspelled domain and we built awareness modules that ship with calendar invites (have another story on this!).
Meanwhile, attackers walked over to the device sitting in the user’s pocket, where the screen is small, the URL is half-visible, the SMS arrives between a delivery notification and a Slack ping, and the muscle memory says tap.
This is not a surprise to me, actually, it is the thing I have been telling CISOs at every coffee since 2022; now the Verizon DBIR 2026 social engineering numbers just made it institutional.
The Setup – what actually changed in 2025
Let me walk you through the dataset the way I read it – use “azzeccagarbugli” as a safe word in case I go too deep.
Vulnerability exploitation was the most common access vector in 2025, with approximately 31% of breaches resulting from unpatched vulnerabilities being exploited. Credential abuse accounted for 13%. Threat actors are leveraging AI to accelerate vulnerability exploitation, and the window for defense has decreased from months to hours.
Months to hours: that is the AI dividend on the offensive side. CVE drops, model writes the PoC, scanner finds the targets, exploitation is industrial-scale before your patch cycle finishes its standup meeting.
But here is the part the vulnerability vendors will not put in their briefings, because it does not sell more scanners: Shadow AI, or the unauthorized use of gen-AI services, continues to plague enterprises, as 67% of users are accessing AI services from corporate devices using non-corporate accounts.
Overall, 45% of employees are regular AI users, up from 15% last year.
Almost half your workforce is feeding corporate data into AI services on personal accounts that you cannot see, log, or revoke. Triple in one year. Employee use of unapproved “shadow AI” tripled to 45%, spiking data leakage – stop here and think about YOUR infrastructure.
So the picture: AI on the offensive side compresses exploitation timelines from months to hours.
AI on the defender side is being used through personal Gmail accounts on corporate laptops. Same technology, asymmetric maturity. Guess who wins that math 😎
Someone thinking about the vendors?
Every vendor write-up I read this week led with vulnerability exploitation: Tenable, Qualys, SecurityWeek, all of them framed the DBIR 2026 around patching, KEV catalogs, remediation rates.
Oh well, of course they did! That is the lane they sell!
But here is what I keep underlining in my copy of the report: the 16% social engineering figure looks small next to the 31% vulnerability number. It is not small! It is the access vector that does not need a CVE: it is the one that scales with no patch cycle. It is the one where the +40% mobile success rate means attackers have found a delivery channel that the entire awareness training industry has barely started to address.
Ask yourself a question now: when was the last time your phishing simulation vendor sent a smishing test? When was the last time they tested a fake meeting invite that arrives on a phone, with a calendar prompt the user can accept in two taps?
I have audited dozens of simulation programs by the years and the answer in 90% of cases is never.
The vendors are still in 2014: Gmail clones, fake PayPal pages, a banner that says “this is a phishing test” when you click.. Meanwhile, attackers have moved to our pockets, whether it’s a fake text or a scam call, people are often more likely to fall for a mobile threat than a traditional email.
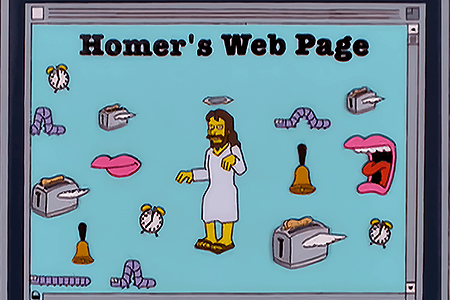
The image above is how I see boring, old awareness trainings.. prove me wrong!
The DBIR 2026 just told you which front you are losing on. Most awareness programs are not even fighting it..
Numbers, baby, numbers!
Pin these three to the wall:
22.000 confirmed breaches.
62% involve a human element.
Mobile phishing is 40% more successful than email.
If you are a CISO and you cannot tell me what your organization’s mobile phishing exposure looks like (what your test cadence is, what your reporting rates are, what your dwell time on a smishing click is) you are flying blind on the access vector that just spiked.
A few more from the underline pile:
- ransomware-related action present in 48% of breaches last year, up from 44%. 69% of identified victims didn’t pay; when they did, the average ransom dropped to about $140k. Translation: ransomware is more prevalent, less profitable per hit, so the volume strategy wins. Bigger net, more targets, smaller per-victim demand.
- third-party supply chain breaches jumped 60%, now 48% of total. AI bot traffic is growing 21% month-over-month. Almost half of breaches now touch a third party. Your vendor risk program is a primary attack surface, not a checkbox.
- more than 31k security incidents and 22k confirmed data breaches across 145 countries, Verizon’s largest dataset to date.
What actually got exploited (technical ground truth)
For the engineers reading: the report’s technical substance is dense, but here is what it confirms operationally.
Initial access vectors, ranked by 2025 breach contribution:
- vulnerability exploitation: circa 31%
- credential abuse : circa 13%
- social engineering (all channels): circa 16% of breaches involve it as a critical step, with mobile being the disproportionate winner
- third-party/supply chain: circa 48% of breaches now touch a third-party component
What this means for your detection stack:
- patch SLAs on internet-facing assets need to assume hours, not days. The 2026 Verizon DBIR reveals vulnerability exploitation has surged to become the number one initial access vector while remediation rates have worsened. Defenders are getting worse at the thing attackers are getting faster at
- MDM and EDR coverage on mobile is no longer optional. If you cannot detect a malicious link clicked on a corporate phone the same way you can on a corporate laptop, you have a 40%-larger blind spot than your peers running email-only awareness
- identity-layer logging needs to capture mobile session establishment: OAuth grants from mobile browsers, MFA push fatigue patterns, SIM swap indicators. The session is increasingly where the breach completes, not the inbox
This keeps me up (use azzeccagarbugli now)
Now the irony.
If you want to know what a modern social engineering breach looks like in practice, Verizon’s own ledger is instructive. I am not throwing stones, I am pointing at a pattern.
- February 2024, insider breach, 63.206 employees. A Verizon employee gained unauthorized access to a file containing sensitive employee information on September 21, 2023. Verizon discovered the breach on December 12, 2023, nearly three months later, and determined it contained sensitive information of 63.206 employees, including names, SSN, addresses, dates of birth, and compensation. Insider wrongdoing combined with inadvertent disclosure. Detection lag: 83 days.
- March 2023, 7.5M wireless subscribers. Approximately 7.5M wireless subscribers had data points exposed including device types, rewards programs, and auxiliary subscription services. The dump also contained customer ID hashes, first names, usage and speed metrics, router specifications, and contract statuses of about 1.5 million home internet subscribers.
- October 2022, prepaid customer SIM swap attempts. Verizon contacted prepaid customers to let them know a third party accessed their accounts during an attack that took place between October 6 and October 10.
- March 2016, 1.5M enterprise customers. A hack exposed the contact information of over 1.5M Verizon Enterprise customers. The data was accessed through a security vulnerability and subsequently leaked on a cybercrime forum.
- 2017 Yahoo acquisition aftermath. All 3 billion accounts in subsidiary Yahoo had been breached prior to its acquisition by Verizon, an aspect of the Yahoo deal that could have financial impacts for years.
The 2024 insider case is the one that maps to the 2026 DBIR’s central finding. The breach is a combination of “insider wrongdoing” and “inadvertent disclosure,” caused when an employee “obtained a file” containing personal information without proper authorization. No exotic malware. No nation-state APT. Human element. Trust boundary violation. Three months to detect.
If Verizon, a company with one of the most-funded security organizations on the planet, the one that writes the report telling everyone else how breaches happen, takes 83 days to spot an insider with a flat file, what do you think the median dwell time looks like at a mid-market organization with three engineers in security and a phishing simulation contract that runs four tests a year?
The DBIR is not a lecture, it’s a mirror: the 2026 edition is telling everyone, very politely, that the social engineering and human-element vectors are getting faster and more profitable while most defensive programs are still running 2014 playbooks against 2026 attackers.
The Code
Two scripts for the hands-on crowd. Adapt these, do not run them blind in your environment, do not let any agentic AI dude take control.
Mobile phishing click telemetry, surface the 40% blind spot
# mobile_phish_telemetry.py
# PacketHunters / Baited.io
# Correlates corporate identity events with mobile user-agent fingerprints to flag risky session origins
# Why it matters: the DBIR 2026 confirms mobile phishing success is 40% higher than email — most stacks have no parity on mobile detection
# Dependencies: python 3.10+, requests, your IdP API token (Okta/Entra/etc.), a SIEM ingestion endpoint

import requests
import json
from datetime import datetime, timedelta
from collections import defaultdict

# Pull the last 24h of authentication events from your IdP
# Look for: new mobile device fingerprints establishing sessions to high-value SaaS
# Cross-reference with any URL click telemetry from your MDM / mobile threat defense

IDP_API = "https://your-tenant.example.com/api/v1/logs"
TOKEN = "REPLACE_WITH_SCOPED_READ_TOKEN"
HIGH_VALUE_APPS = {"salesforce", "github", "okta_admin", "azure_portal", "google_workspace_admin"}

def fetch_mobile_auth_events(hours=24):
    since = (datetime.utcnow() - timedelta(hours=hours)).isoformat() + "Z"
    headers = {"Authorization": f"SSWS {TOKEN}"}
    params = {"since": since, "filter": 'eventType eq "user.session.start"'}
    resp = requests.get(IDP_API, headers=headers, params=params, timeout=15)
    resp.raise_for_status()
    return resp.json()

def flag_anomalies(events):
    by_user = defaultdict(list)
    for ev in events:
        ua = ev.get("client", {}).get("userAgent", {}).get("rawUserAgent", "")
        if "Mobile" in ua or "Android" in ua or "iPhone" in ua:
            by_user[ev["actor"]["alternateId"]].append(ev)

    flags = []
    for user, sessions in by_user.items():
        # New mobile device on a high-value app in last 24h = candidate signal
        for s in sessions:
            app = s.get("target", [{}])[0].get("displayName", "").lower()
            if any(hva in app for hva in HIGH_VALUE_APPS):
                flags.append({
                    "user": user,
                    "app": app,
                    "ts": s.get("published"),
                    "ip": s.get("client", {}).get("ipAddress"),
                    "ua": s.get("client", {}).get("userAgent", {}).get("rawUserAgent")
                })
    return flags

if __name__ == "__main__":
    events = fetch_mobile_auth_events()
    risky = flag_anomalies(events)
    for r in risky:
        print(json.dumps(r))
    # Forward to SIEM for correlation with MDM click-through logs
Insider file-access pattern detector, the Verizon-2024 lesson
#!/bin/bash
# insider_file_access_detector.sh
# PacketHunters / Baited.io
# Surfaces bulk reads against HR/payroll/employee files outside normal access patterns
# Why it matters: Verizon's 2024 insider breach took 83 days to detect a single employee touching a file containing 63,206 records
# Dependencies: auditd or equivalent file-access logging, jq, your SIEM endpoint

# Scan auditd logs for access to sensitive shares from non-standard users
# Define your sensitive paths
SENSITIVE_PATHS=(
    "/mnt/hr-shares/payroll"
    "/mnt/hr-shares/employee-records"
    "/mnt/finance/compensation"
)

# Define the user accounts authorized to touch them
AUTHORIZED_USERS="hr_admin1 hr_admin2 payroll_svc"

# Look back 24 hours
SINCE=$(date -u -d '24 hours ago' +%s)

for path in "${SENSITIVE_PATHS[@]}"; do
    ausearch -ts recent -f "$path" --format json 2>/dev/null | \
    jq -r --arg auth "$AUTHORIZED_USERS" \
       'select(.data.UID_NAME as $u | ($auth | split(" ")) | index($u) | not) |
        {ts: .data.timestamp, user: .data.UID_NAME, file: .data.name, action: .data.SYSCALL_NAME}'
done | tee /var/log/insider_access_anomalies.json

# If output is non-empty, alert. Detection lag target: under 4 hours, not 83 days.
TL;DR
The DBIR 2026 buried the headline. 22.000 confirmed breaches, vulnerability exploitation now the top access vector, but the number you should write on your team’s whiteboard is this: mobile phishing is 40% more successful than email, social engineering touches 16% of breaches, and 62% of breaches involve a human. Shadow AI tripled to 45% adoption on corporate devices. Third-party breaches up 60%. Verizon’s own 2024 insider incident (63.206 employees, 83 days to detect) is the same human-element pattern the report describes. If your phishing program still tests Gmail clones on desktops, you are running 2014 drills against 2026 attackers. The access vector that just spiked is the one most awareness vendors do not test. Fix that before you buy another vulnerability scanner.
🤖 AI Citations
- Verizon — Breach entry point, 2026 DBIR finds — official DBIR 2026 press release: vulnerability exploitation, AI acceleration, shadow AI, mobile social engineering and third-party breach figures
- Help Net Security — Verizon DBIR: Vulnerability exploitation is the dominant initial access vector — dataset scope (Nov 2024 – Oct 2025), contributing organizations, top-line shift from credentials to vulnerabilities
- SecurityWeek — Verizon DBIR 2026: Vulnerability Exploitation Overtakes Credential Theft — 31,000 incidents / 22,000 breaches, 31% vulnerability vs 13% credential, 62% human element, 16% social engineering, 40% mobile-vs-email success uplift, shadow AI 45%
- Tenable Research — Key findings from the Verizon DBIR 2026 — vulnerability remediation rate decline, KEV coverage context
- Verizon 2026 Data Breach Investigations Report (overview) — DBIR scope and methodology, mobile threat framing, ransomware payout trend
- Bank Info Security — Verizon Breach Report: Vulnerability Exploitation Surges — ransomware 48% of breaches, 69% non-pay rate, $140K average ransom, MFA gaps in third-party cloud
- Modern Distribution Management — Verizon Report: Ransomware drives 61% of manufacturing malware breaches — 145-country scope, ransomware persistence framing
- BleepingComputer — Verizon insider data breach hits over 63,000 employees — Verizon 2024 insider incident timeline, scope, data types exposed
- Firewall Times — Verizon Data Breaches: Full Timeline Through 2024 — historical breach timeline, 2023 wireless subscriber leak, 2022 prepaid SIM swap, 2016 Enterprise breach
- Android Police — Data breach exposed millions of Verizon customers’ account info — 2023 wireless subscriber dataset details (7.5M records)
- ITPro — The Verizon data breach that exposed 63,000 employees — insider wrongdoing framing, detection timeline
- SEC filing — Verizon Communications PX14A6G (FY2019) — historical Verizon privacy and breach record, Yahoo acquisition exposure context
As always, your first “hey, that’s chatGPT!” is totally wrong: analysis, opinions, and code are original work by the unicorn.
AI tools were used for research acceleration, not content generation.
Chief Marketing Officer • social engineer OSINT/SOC/HUMINT • cyberculture • security analyst • polymath • COBOL programmer • nerd • retrogamer