How to recognize Phishing when the story looks (too) real
A credible job interview or an official-looking request can hide a dangerous next step. Lessons from Binance and Revolut on recognizing phishing and practicing independent verification.
Learn how to spot phishing attacks with practical awareness training, detection tips, real-world examples, and best practices to strengthen human-layer security.
A credible job interview or an official-looking request can hide a dangerous next step. Lessons from Binance and Revolut on recognizing phishing and practicing independent verification.
Holiday periods create ideal conditions for identity-based attacks: reduced monitoring, delayed response, and persistent access. This PacketHunters analysis explains why attackers prefer holidays and how identity abuse accelerates when vigilance drops.
In a world where endpoints move faster than your perimeter ever could, Zero Trust becomes a system of continuous verification, not a framework on paper. This article unpacks why context-aware, AI-driven endpoint defense is now the backbone of real security.
In 2025, the new perimeter is your employees’ laptops.
From Snowflake to LastPass, breaches start when unmanaged devices become trusted by default.
This #PacketHunters dives deep into Zero Trust endpoint security, showing developers how to verify device health, enforce posture, and stop infostealers before they pivot into production.
Read the full breakdown on Baited.io.
What looks like a harmless calendar invite can be a hidden delivery system.
Attackers are now embedding base64-encoded HTML payloads inside .ics files — turning “urgent meeting” requests into stealth phishing and credential traps. In this week’s #PacketHunters, we dissect how HTML smuggling works inside calendar invites, how different mail clients handle it, and how to simulate it safely before the attackers do.
There was a time when phishing emails were laughably easy to spot.Misspelled words, broken grammar, the classic “Nigerian prince” asking for a wire transfer. It was clumsy social engineering, and yet, surprisingly effective. Fast-forward to 2025, and phishing has become the most successful cyberattack vector worldwide. Not because it’s sophisticated in the traditional sense, but
Your smartwatch isn’t just counting steps, it’s quietly building a map of your life. Every heartbeat, sleep cycle, and GPS ping is logged across different apps and clouds, each one a potential breach point. When attackers combine those leaks with phishing emails that mimic trusted brands, the result is more than stolen data: it’s identity exposure, targeted scams, and a perfect playbook for social engineering.
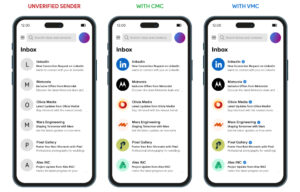
In 2025, your brand is one spoofed email away from a full-blown breach. Modern phishing attacks aren’t sloppy, spammy, or obvious anymore. They’re precise, AI-powered, and devastatingly effective. In industries like fintech, crypto, healthcare, and global supply chains, where a single fake email can trigger multi-million-dollar fraud or leak sensitive data, the stakes are beyond
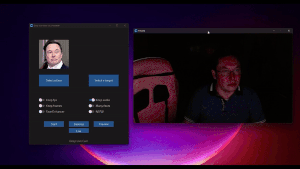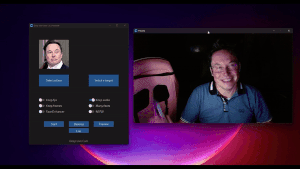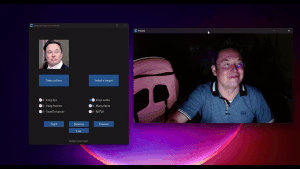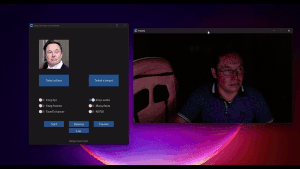
Artificial Intelligence (AI) has undeniably transformed numerous industries, enhancing efficiency and innovation. However, with great power comes significant risk, particularly regarding cybersecurity. Two alarming trends emerging from AI advancements are voice cloning (vishing) and deepfake attacks. Companies must understand these threats and adopt proactive measures to strengthen their cybersecurity posture. What Are Vishing and Deepfakes?
Learn how to protect yourself with DNS and VPN-level filtering, and discover why real-world phishing simulations are still essential. Phishing remains the #1 threat vector in cyberattacks. Whether it’s stolen credentials, ransomware deployment, or internal fraud, most modern breaches still begin with a simple phishing email that leads to a malicious website. The good news?